Your security tools generate more alerts than any internal team can realistically triage, and once an intrusion starts, it can move from first access to full compromise in minutes, not days. Building and staffing a 24/7 Security Operations Center in-house is out of reach for most mid-sized organisations, yet NIS2, DORA and GDPR increasingly expect you to prove someone is watching. Without continuous monitoring, the one alert that matters gets lost in the noise.
Your concerns, our answers
Isn’t 24/7 monitoring only within reach of large enterprises?
Not anymore. A Managed SOC gives mid-sized organisations enterprise-grade monitoring at a predictable, per-endpoint cost, without hiring and rostering a round-the-clock team yourself.
How do I know a real threat won’t get lost in all of the noise?
Automated correlation filters the noise first; a human analyst validates every real alert before it reaches you, and recurring false positives can be suppressed entirely at your request.
Does outsourcing monitoring mean losing control of our NIS2 or DORA compliance?
No, you remain the accountable party. Our SOC operates under a documented governance framework, with regular reporting designed to support your NIS2, DORA and ISO 27001 evidence.
Already running a SIEM no one has time to watch, or drowning in alerts from tools that don’t talk to each other?
Belgian-developed, EU-hosted SOC platform and SIEM, built with data sovereignty in mind.
We own our detection engine and SIEM layer, rather than reselling someone else’s platform.
24/7 human-led threat hunting, supported by AI-based tooling, not replaced by it.
Trusted partner to the Centre for Cybersecurity Belgium (CCB), with active ties to KU Leuven, VUB and UCL.
Continuous, correlated monitoring across endpoint, network, identity, cloud and DNS, so a threat that crosses systems doesn’t slip through the gap between separate tools.
Tier 1 to Tier 3 analysts and threat hunters validate every real alert and contain confirmed threats, pairing automated containment with human judgement rather than relying on either alone.
It continuously monitors your endpoints, network, identity, cloud and DNS traffic, correlates that telemetry into real alerts, and has an analyst investigate and contain anything confirmed as a genuine threat, around the clock.
Is a Managed SOC only worth it for large enterprises?
No, if anything the opposite. Mid-sized organisations often get the most value: large enough to be a real target and to fall under NIS2, but rarely with the budget or headcount to run a 24/7 SOC in-house. (Not sure where your organisation stands under NIS2? /solutions/grc)
What happens once you detect a real threat?
Depending on severity, we act immediately through automated containment, such as isolating a compromised device, while an analyst investigates in parallel. You’re notified and kept updated throughout, not only after the fact.
Where is my data hosted, and what does that mean for GDPR?
Your telemetry is processed through our Belgian-developed SIEM and hosted in the EU.
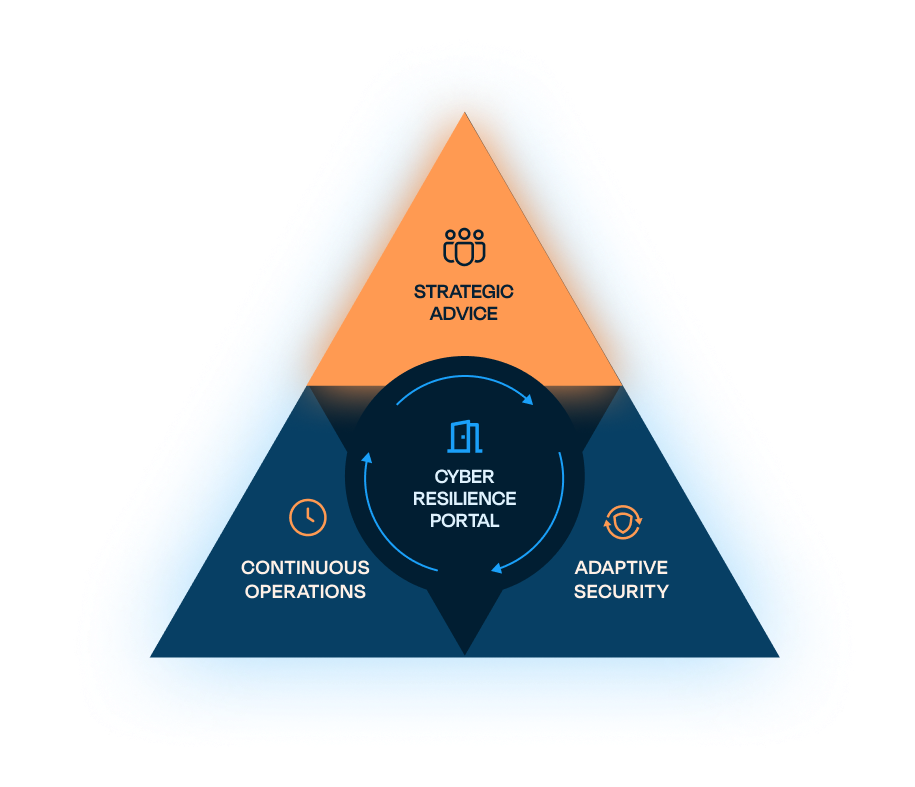
The Triangle of Cyber Resilience
Security Operations Center (SOC) is part of Continuous Operations, Approach Cyber’s pillar for ongoing vigilance and validation, alongside our Phishing & Awareness, Vulnerability & Exposure Management, DFIR, Managed Firewall Services and Offensive Security teams. Continuous Operations validates, in real time, what Strategic Advice designed and Adaptive Security enforced.