Sooner or later, most organisations face a serious cyber incident, and what happens in the first hour often decides the outcome. Without a clear escalation plan or an external team on call, every hour of delay compounds the financial loss, slows recovery, and increases your exposure under GDPR, DORA and NIS2. Monitoring tells you something happened; it doesn’t respond to it, and that gap is where the real damage happens.
Your concerns, our answers
We’ve been hit by ransomware, who do I call now?
Our 24/7 hotline: a live person answers within 30 minutes, and we open an incident-management meeting remotely within about an hour.
Should I pay the ransom, or negotiate with the attackers?
We don’t negotiate directly, in line with Belgian law and FIRST.org guidance, but we help you weigh the decision and can bring in a trusted specialist partner if you choose to.
We already have monitoring in place, isn’t that enough?
Monitoring tells you something happened; it doesn’t contain it or investigate it. Our DFIR team does both, and helps you meet your GDPR, NIS2 and DORA reporting obligations at the same time.
Already have a cyber insurance policy or an internal SOC, and hoping you’ll never actually need to use either?
One of only 10 FIRST.org-accredited CSIRT teams in Belgium: peer-audited, with global threat-intelligence sharing.
24/7 hotline with documented SLAs: human response within 30 minutes, an incident-management meeting within about an hour, on-site support in Belgium within 4 hours.
Technical investigation and GDPR/DORA/NIS2 breach-management expertise from one team, not stitched together from two separate providers.
Already run an internal SOC? We act as your Tier 3 escalation and forensic surge, so you don’t have to build that capability yourself.
A readiness assessment, response playbooks, an agreed escalation contact list, and monthly reviews with a dedicated delivery manager, so you know exactly who to call and what happens next, before you ever need to.
A live person answers our hotline within 30 minutes, an incident-management meeting follows within about an hour, and on-site support in Belgium arrives within 4 hours when needed, all under a documented SLA.
No retainer in place? We can still respond to an active incident on a time-and-materials basis, with a clear, tracked plan of hours agreed with you as the investigation develops.
In-depth forensic investigation, malware analysis and attack-timeline reconstruction, including support for legal, insurance or litigation proceedings.
Breach qualification, risk assessment and support preparing your notification to the data protection authority, coordinated with your DPO and legal advisors.
A live person answers within 30 minutes, and we open an incident-management meeting remotely within about an hour. From there, we work in parallel on containment, investigation, and your regulatory notification obligations; on-site support in Belgium follows within 4 hours if the situation needs it.
Do I need a retainer in place before you can help?
No. We can respond to an active incident on an ad-hoc basis without a retainer already in place. A retainer gets you a documented SLA, readiness playbooks and an agreed contact list before a crisis, rather than during one, which is where most of the time is usually lost.
Do you handle the GDPR breach notification for us?
We support you throughout: qualifying the breach, assessing the risk, and preparing what you need to notify the data protection authority within the legal deadline. The final notification decision and liability remain yours. Not sure where your organisation stands on GDPR or NIS2? See our GRC page.
What if we don’t already have logging or monitoring in place?
We can still help, but forensic depth depends on it: without basic endpoint and network logs, we can often confirm an incident happened without being able to establish its full root cause or scope. Our SOC or a readiness assessment can help close that gap before it matters.
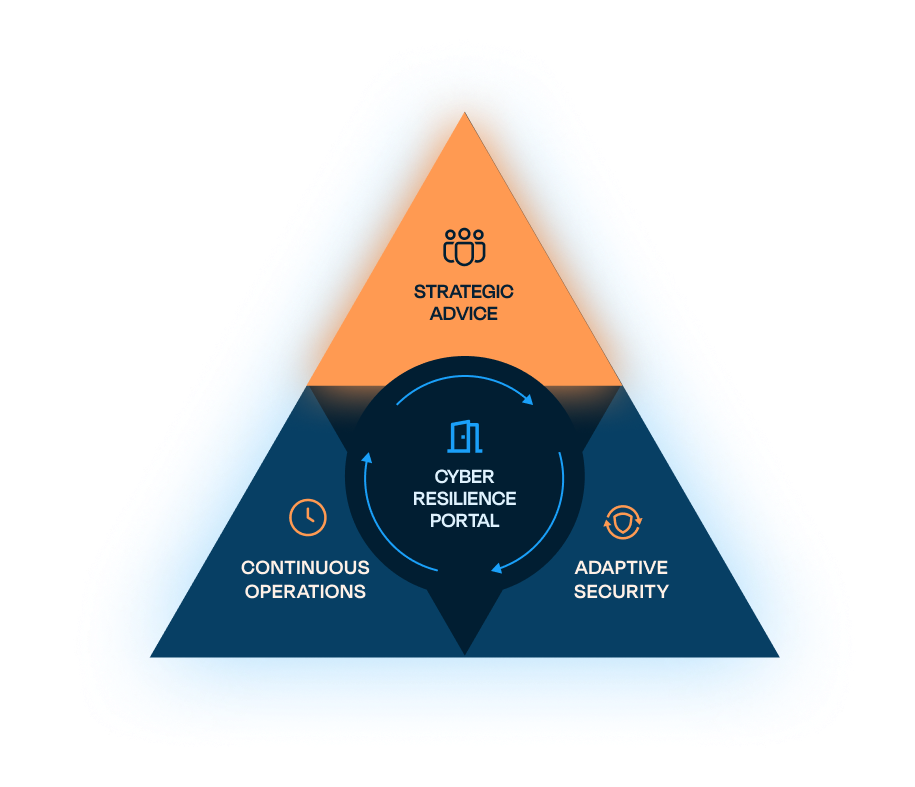
The Triangle of Cyber Resilience
Digital Forensics & Incident Response (DFIR) is part of Continuous Operations, Approach Cyber’s pillar for ongoing vigilance and validation, alongside our SOC, Phishing & Awareness, Vulnerability & Exposure Management, Managed Firewall Services and Offensive Security teams. Continuous Operations validates, in real time, what Strategic Advice designed and Adaptive Security enforced.