Phishing and social engineering increasingly target your staff, not your firewall, and one careless click can trigger a data leak, a fraudulent payment, or a full breach such as CEO fraud. Safeonweb, Belgium’s national reporting centre, received nearly 10 million suspicious-message reports in 2025 (source), and NIS2, DORA and GDPR now expect you to prove your employees are trained to spot it. Technology alone cannot close that gap.
Your concerns, our answers
Would my employees actually spot a phishing email?
Most people can’t yet. Regular simulations and training measurably improve click and report rates over time.
Are we meeting our NIS2 or DORA awareness obligations?
Not with a single training session. Our managed programmes combine ongoing simulations with continuous training, built to support both.
What about our senior management and the board?
They’re often targeted specifically. We run dedicated spear phishing simulations and training for leadership, alongside frontline staff.
Already run occasional phishing tests, or rely on a generic e-learning platform?
Campaigns designed by active cybersecurity professionals using current European threat intelligence, not generic templates.
Delivered from Belgium and Switzerland, with your phishing simulation and training data kept within the EU.
KnowBe4 and Phished.io partner, and Microsoft Security Partner.
Builds on Controlled Awareness with deeper customisation and management reporting: bespoke phishing scenarios and spear phishing simulations for senior management and the board, tailored to your specific content and reporting needs.
How do you measure whether awareness training is working?
We track how your organisation improves over time, comparing click and report rates across simulations, and translate the results into reporting suitable for management and board audiences.
Is phishing simulation enough to meet my NIS2 or DORA awareness requirements?
No. Both NIS2 and DORA expect ongoing awareness measures, not a single training session. Our managed programmes combine regular simulations with continuous training, built to support both obligations. Not sure where your organisation stands on NIS2 or DORA?
Can this include senior management and the board?
Yes. We run targeted spear phishing simulations for senior management and the board, alongside frontline staff training.
Where is my phishing simulation and training data stored?
Within the EU. Our KnowBe4 environment runs in EU data centres (Frankfurt or Dublin), contractually set to the EU region for every client; our Phished.io environment is run by a Belgian company.
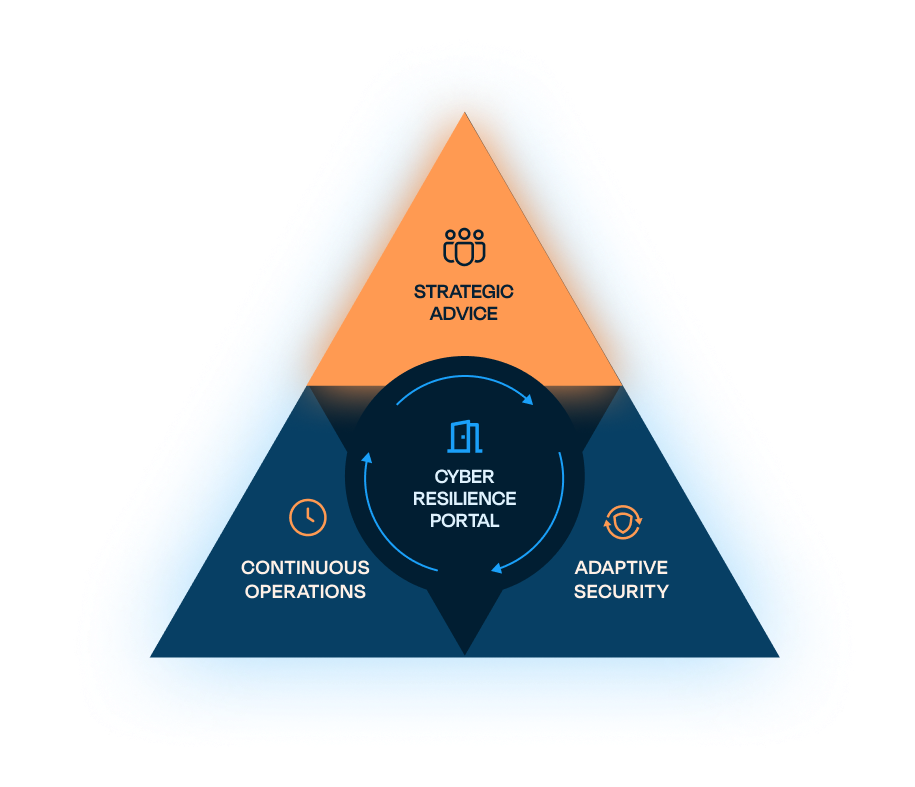
The Triangle of Cyber Resilience
Phishing & Awareness is part of Continuous Operations, Approach Cyber’s pillar for ongoing vigilance and validation, alongside our SOC, DFIR, Vulnerability & Exposure Management, Managed Firewall Services and Offensive Security teams. Continuous Operations validates, in real time, what Strategic Advice designed and Adaptive Security enforced.