Regulators are tightening cyber obligations under NIS2, DORA, the Cyber Resilience Act, the AI Act and GDPR, and increasingly hold your management team personally accountable when they aren’t met, not only the business. At the same time, generative AI is making attacks more convincing, and customers, investors and partners increasingly expect proof that you take security and compliance seriously before they trust you with their data or their money. Without a governance structure that keeps risk, compliance and incident readiness under continuous ownership, the gaps go unnoticed until a regulator, an auditor or an attacker finds them first.
Your concerns, our answers
We’re being asked for proof of our cybersecurity. What do we actually give them?
A recognised certification or audited compliance report, such as ISO 27001, backed by the management system that keeps it valid year after year, not a one-off audit.
We can’t justify a full-time CISO, but we need that level of oversight.
Our CISO as a Service gives you an experienced CISO and a supporting team, covering strategy, risk, compliance and incident response, without the cost of a full-time hire.
One of our suppliers could be our weakest link, and NIS2 makes us responsible for that too.
We continuously assess and manage the cyber risk in your supply chain, so you can demonstrate that oversight rather than just assume it.
Already juggling a growing list of regulations and standards, and not sure which ones actually apply to you?
Consultants experienced across a broad range of industries and environments, so the approach we recommend is pragmatic, not generic.
Coverage across NIS2, DORA, the Cyber Resilience Act, the AI Act, eIDAS and the EU Whistleblower Directive.
Expertise across ISO 27001, ISO 22301, Cyber Fundamentals, ISA62443, CMMC, TISAX, CIS Controls, NIST and SOC2.
Cyber security diagnostics and compliance evaluations against the regulations, laws, industry practices and standards that apply to you, giving you a clear, risk-based view of where you stand and an actionable plan to close the gaps. For investors, this extends to security ratings and cyber due diligence support ahead of a transaction.
Ongoing strategic guidance and hands-on delivery, either as an extension of your existing CISO, or, if you don’t have one, as a fully outsourced CISO function covering strategy, risk management, compliance and incident response.
We lead and support your compliance effort against the laws, regulations and standards that apply to you, implementing, auditing and improving your management systems on the way to certification, including a dedicated, EU-hosted reporting channel and outsourced liaison agent for the EU Whistleblower Directive.
Continuous assessment and management of the cyber risk in your supply chain, aligned with NIS2, so you can identify weak links before they become yours and demonstrate that oversight to your own customers.
ISO-aligned business continuity and disaster recovery plans, tested through regular drills and audits, alongside incident response and crisis management plans that meet your NIS2 and GDPR reporting obligations, backed by training and tabletop exercises.
Essential entities can face fines of up to €10 million or 2% of global annual turnover, whichever is higher; important entities face up to €7 million or 1.4% (source). Several member states also introduce personal liability for management. [TO CONFIRM: verify current national transposition status before publishing.] Not sure whether NIS2 applies to your organisation in the first place? Read more on our Strategic Advice page →
My clients or partners are asking for proof of our cybersecurity - what do I actually give them?
A recognised certification such as ISO 27001, or an equivalent framework, backed by the management system that keeps it valid year after year. We help you choose the right standard for your sector and lead you through implementation, internal audit and certification.
We can’t justify hiring a full-time CISO - is CISO as a Service actually enough?
For most SMEs, yes. You get an experienced CISO and a supporting team, covering strategy, risk, compliance and incident response, at a fraction of the cost of a full-time hire, and the engagement scales as your organisation and its obligations grow.
What is a cyber incident response plan, and do I still need one if we already work with a SOC?
A cyber incident response plan sets out who does what in the first hours and days of an incident, including your NIS2 and GDPR notification deadlines. A SOC detects and monitors; it doesn’t replace that plan. We help you design and test one, including tabletop exercises, alongside our SOC and DFIR teams for when it’s needed for real.
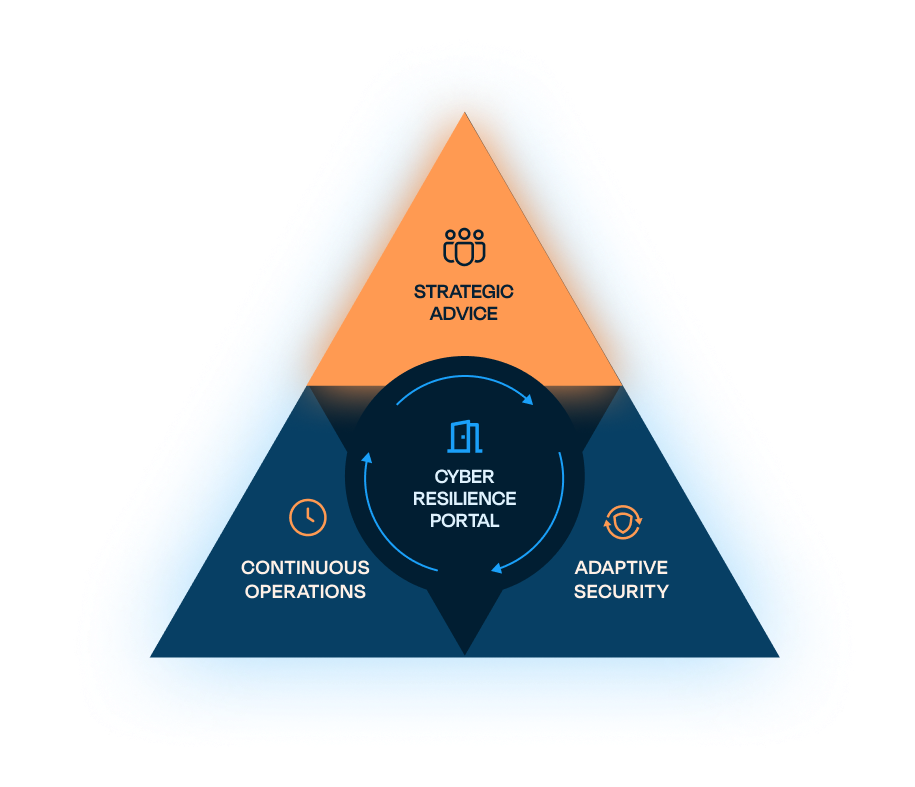
The Triangle of Cyber Resilience
Governance, Risk & Compliance (GRC) is part of Strategic Advice, Approach Cyber’s pillar for setting the direction of your cyber resilience strategy, alongside our Security Architecture team. Strategic Advice defines what Adaptive Security then puts into practice, and Continuous Operations validates every day.