In this era, security alone is no longer the goal, continuity is. Your business needs to be able to withstand attacks, detect them in seconds, and recover without losing its licence to operate, whether that means meeting a regulatory obligation, or designing security into your architecture from the start. Resilience begins with strategy, not tooling.
If you build or embed software, security by design is now a regulatory expectation, not just good practice. We design it into your architecture from the start.
From a risk assessment that tells you what to protect first, to turning NIS2, GDPR, ISO and Cyber Resilience Act obligations into a clear, practical roadmap backed by CISO as a Service for day-to-day governance support.
We design the blueprint for your digital continuity, integrating your technical and operational layers by design the same principle regulations like the Cyber Resilience Act now require for the products and software you build.
Where do I start with cybersecurity for my business?
Start with a risk assessment: it tells you what to protect first and how much to invest, before you buy any tool. Our GRC and Security Architecture teams build that roadmap with you.
Does NIS2 apply to my company?
NIS2 applies to a wide range of medium and large organisations in essential and important sectors, and increasingly to their suppliers. If you’re not sure where your organisation stands, a short scoping check is the fastest way to know.
Does the Cyber Resilience Act (CRA) apply to my organisation?
The CRA applies broadly to anyone who develops, manufactures or sells products with digital elements in the EU, not just software vendors. If you build or embed software as part of what you sell, it’s worth checking your obligations early: our GRC team can confirm your scope, and our Security Architecture team can help you build security by design.
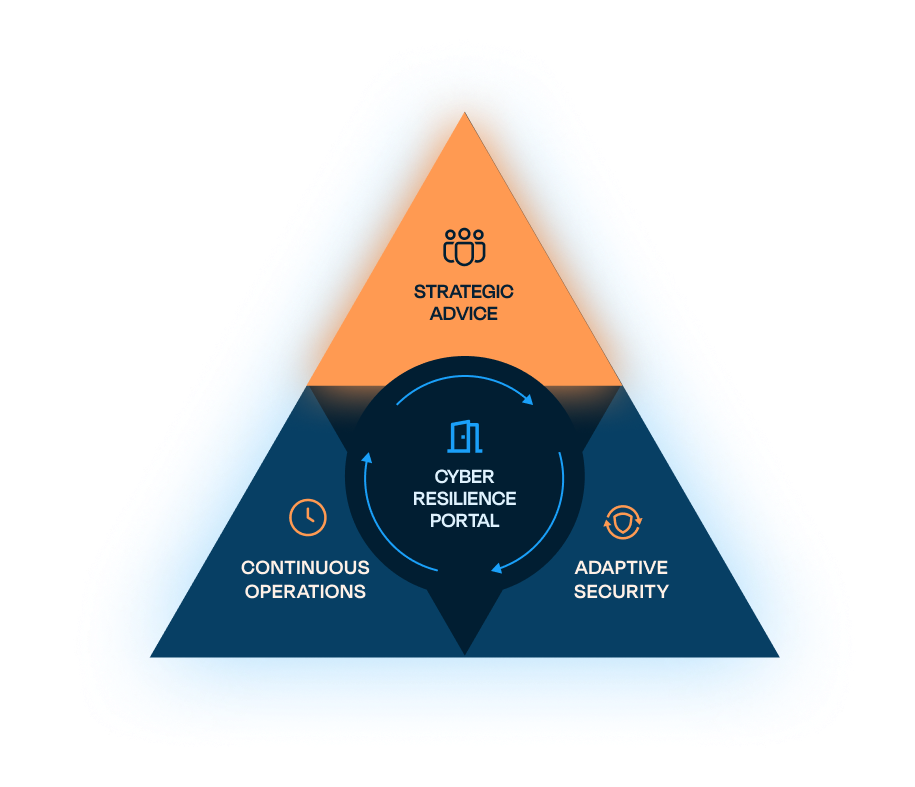
The Triangle of Cyber Resilience
Strategic Advice defines your cyber resilience strategy. Adaptive Security puts that strategy into practice, while Continuous Operations validates it every day. Each pillar picks up where the previous one left off.