Regulators are tightening cyber obligations under NIS2, DORA, the Cyber Resilience Act, the AI Act and GDPR, and increasingly hold your management team personally accountable when they aren’t met. Meanwhile generative AI is making attacks more convincing, and customers, investors and partners expect proof that you take security and compliance seriously before they trust you with their data or their money. Without clear, continuous ownership of risk, compliance and incident readiness, the gaps will continue to go unnoticed until a regulator, an auditor or an attacker finds them.
Your concerns, our answers
We’re being asked for proof of our cybersecurity. What do we actually give them?
A recognised certification or audited compliance report, such as ISO 27001, backed by the management system that keeps it current year after year, not a one-off audit.
We can’t justify a full-time CISO, but we need that level of oversight.
Our CISO as a Service gives you an experienced CISO and a supporting team, covering strategy, risk, compliance and incident response, without the cost of a full-time hire.
One of our suppliers could be our weakest link, and NIS2 makes us responsible for that too.
We continuously assess and manage cyber risks in your supply chain, so you can demonstrate oversight rather than just assume it.
Already juggling a growing list of regulations and standards, and not sure which ones actually apply to you?
Consultants with experience across a wide range of industries , so our advice is pragmatic, not generic.
Coverage of NIS2, DORA, the Cyber Resilience Act, the AI Act, eIDAS and the EU Whistleblowing Directive.
Expertise in ISO 27001, ISO 22301, CyberFundamentals, ISA/IEC 62443, CMMC, TISAX, CIS Controls, NIST and SOC 2.
Cybersecurity diagnostics and compliance assessments against the laws, regulations and standards that apply to you, giving you a clear, risk-based view of where you stand and an actionable plan to close the gaps. For investors, we also provide security ratings and cyber due diligence ahead of a transaction.
Ongoing strategic guidance and hands-on delivery, either supporting your existing CISO, or, if you don’t have one, as a fully outsourced CISO function covering strategy, risk management, compliance and incident response.
We guide and support your compliance with applicable laws, regulations, and standards, by implementing, auditing, and improving your management systems all the way to certification.
For the EU Whistleblowing Directive, we also provide a dedicated, EU-hosted reporting channel and an outsourced liaison agent.
Continuous assessment and management of cyber risks in your supply chain, aligned with NIS2, so you can spot weak links before they become problematic and demonstrate that oversight to your own customers.
ISO-aligned business continuity and disaster recovery plans, tested through regular drills and audits, plus incident response and crisis management plans that meet your NIS2 and GDPR reporting obligations, all backed by training and tabletop exercises.
Essential entities can face fines of up to €10 million or 2% of their global annual turnover, whichever is higher; important entities can face up to €7 million or 1.4% (source). Several Member States also introduced personal liability for management.
My clients or partners are asking for proof of our cybersecurity posture - What do I actually give them?
A recognised certification such as ISO 27001, or an equivalent framework, backed by the management system that keeps it valid year after year. We help you choose the right standard for your sector and guide you through the implementation, internal audit and certification.
We can’t justify hiring a full-time CISO - Is CISO as a Service actually enough?
For most SMEs, yes. You get an experienced CISO and a supporting team, covering strategy, risk, compliance and incident response, at a fraction of the cost of a full-time hire. The engagement scales as your organisation evolves and its obligations grow.
What is a cyber incident response plan, and do I still need one if we already work with a SOC?
A cyber incident response plan sets out who does what in the first hours and days of an incident, considering NIS2 and GDPR notification deadlines. A SOC monitors and detects; it doesn’t replace that plan. We help you design and test one, through tabletop exercises, together with our SOC and DFIR teams, so you are always ready when you need it.
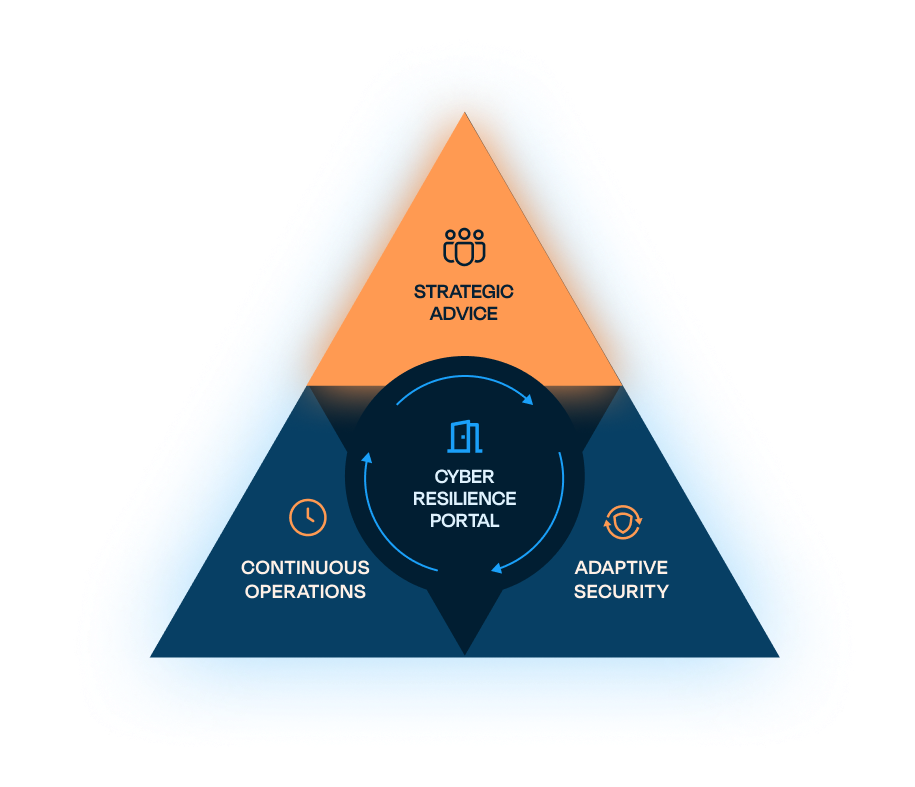
The Triangle of Cyber Resilience
Governance, Risk & Compliance (GRC) is part of Strategic Advice, Approach Cyber’s pillar for setting the direction of your cyber resilience strategy, alongside our Security Architecture team. Strategic Advice defines what Adaptive Security then puts into practice, and Continuous Operations validates every day.