You’ve invested in firewalls, endpoint protection and cloud security, but you’ve never seen how they hold up against someone actually trying to get in. Attackers don’t need anything exotic: over the past year, our ethical hackers ran 142 engagements and logged 952 findings, and not one of them was a zero-day. The weaknesses that let attackers in are usually already there, known and fixable, waiting to be found. With attackers now using AI to scale their techniques, and regulations like DORA requiring threat-led testing for the financial sector, not knowing is no longer an option.
Your concerns, our answers
We already have security tools in place. Isn’t that enough?
Tools tell you what they block, not what they miss. A test shows you how an attacker would chain small gaps across your systems into a real breach, and which ones to fix first.
Won’t we just get a long report full of jargon?
No. Every engagement ends with a report that prioritises what matters and explains how to fix it, and most of our testing is done by hand, so what you receive has been verified by a person, not just flagged by a scanner.
Is red teaming only for banks under DORA?
No. DORA made threat-led testing mandatory for part of the financial sector, but any organisation that wants to know whether its teams would detect and stop a determined attacker can benefit from it.
Not sure whether your defences would stop a real attack, or only a scanner?
80% manual, advanced testing and 20% automated: skilled people, not just tools, find what attackers would.
Methodology grounded in OWASP, OSSTMM, NIST and PTES.
Red teaming and threat-led penetration testing aligned with TIBER-EU, the European framework for simulating real-world attacks.
Five years of published findings: our Pentest Annual Report, now in its 5th edition, shares what we see in the field.
We scan your network for exposed services and common vulnerabilities, then manually verify the results, so you fix the quick wins first and know which systems deserve deeper testing. For continuous scanning, see Vulnerability & Exposure Management.
We simulate real-world attacks on your systems using advanced hacking techniques, and deliver a clear report with prioritised remediation, so you know exactly where you stand and what to fix.
An objective-led test built around a specific threat, such as an employee accessing data they shouldn’t or a social engineering attempt, so you see how your defences hold up against the scenario that worries you most. For employee training programmes, see Phishing & Awareness.
We act as an advanced, persistent attacker over time to test not just your systems, but whether your teams detect and respond. Aligned with TIBER-EU, including for threat-led penetration testing (TLPT) under DORA.
Our attackers (red team) work side by side with your defenders (blue team), so every simulated attack directly improves your detection and response, rather than ending in a report alone.
What’s the difference between a vulnerability assessment and a penetration test?
A vulnerability assessment scans for known weaknesses and tells you what is exposed. A penetration test goes further: an ethical hacker actively exploits those weaknesses, the way a real attacker would, to show what could actually be reached and how much damage could be done.
What’s the difference between a pentest, red teaming and purple teaming?
A pentest looks for as many weaknesses as possible in a defined scope. Red teaming simulates a real, targeted attacker over time, to test whether your teams detect and respond. Purple teaming puts attackers and defenders together, so detection and response improve during the exercise itself.
Does DORA require threat-led penetration testing?
Yes, for financial entities designated by their competent authority: DORA requires threat-led penetration testing on live production systems, at least every three years. We run these exercises using the TIBER-EU framework. Not sure whether DORA applies to you?
How often should we test our defences?
[TO CONFIRM with the offensive team: no source states our recommended frequency. Common practice is at least once a year and after any significant change to your systems or applications; confirm before publishing.]
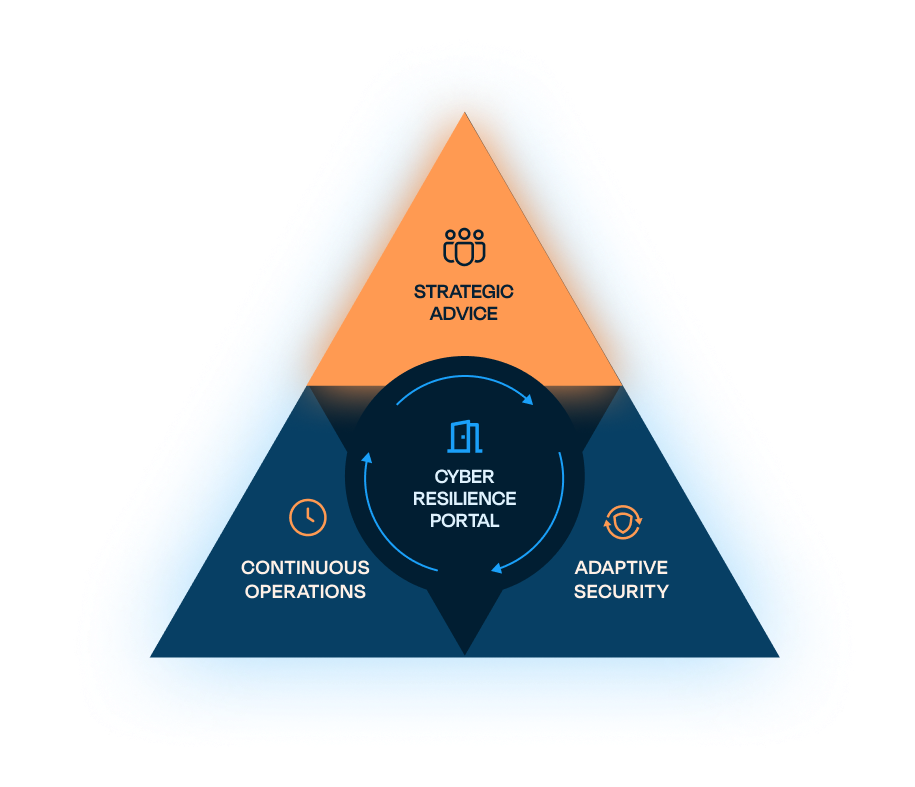
The Triangle of Cyber Resilience
Offensive Security is part of Continuous Operations, Approach Cyber’s pillar for ongoing vigilance and validation, alongside our SOC, Vulnerability & Exposure Management, DFIR, Managed Firewall Services and Phishing & Awareness teams. Continuous Operations validates, in real time, what Strategic Advice designed and Adaptive Security enforced, and offensive testing is the most direct way to prove it holds.