Most organisations build their security one tool at a time, in response to whatever risk feels most urgent that quarter. The result is rarely a coherent defence: it’s a stack of point solutions that don’t talk to each other, leaving gaps that attackers may find long before your own team does. Regulations ,such as the Cyber Resilience Act, expect security to be built into your products and software from the start, not patched on afterwards.
We identify and prioritise potential security threats by analysing the design and architecture of what you’re building, so you can mitigate risks before a vulnerability ever ships.
We help you implement a secure software development lifecycle (SSDLC) and DevSecOps practices, and train security champions within your teams, so security is built in from the very first requirement, not bolted on before release.
Rarely through a single dramatic failure. Most breaches exploit the gaps between tools and systems that were never designed to work together. A security architecture review closes these gaps before an attacker finds them. Not sure where to start assessing your exposure?
Where do I start with cybersecurity for my business?
Start with a risk assessment: it tells you what to protect first and how much to invest, before you buy any tool. Our GRC and Security Architecture teams build that roadmap with you.
What’s the difference between GRC and Security Architecture?
GRC defines what you need to protect and which regulatory obligations you need to meet, such as NIS2 or the Cyber Resilience Act. Security Architecture defines how your technical and operational layers should be built to meet these obligations, ensuring compliance and security are part of the same design decision rather than separate concepts.
Does the Cyber Resilience Act (CRA) apply to my organisation?
The CRA applies broadly to anyone who develops, manufactures or sells digital products in the EU, not just software vendors. If you build or embed software as part of what you sell, our GRC team can confirm your scope, and our Security Architecture team can help you build security by design.
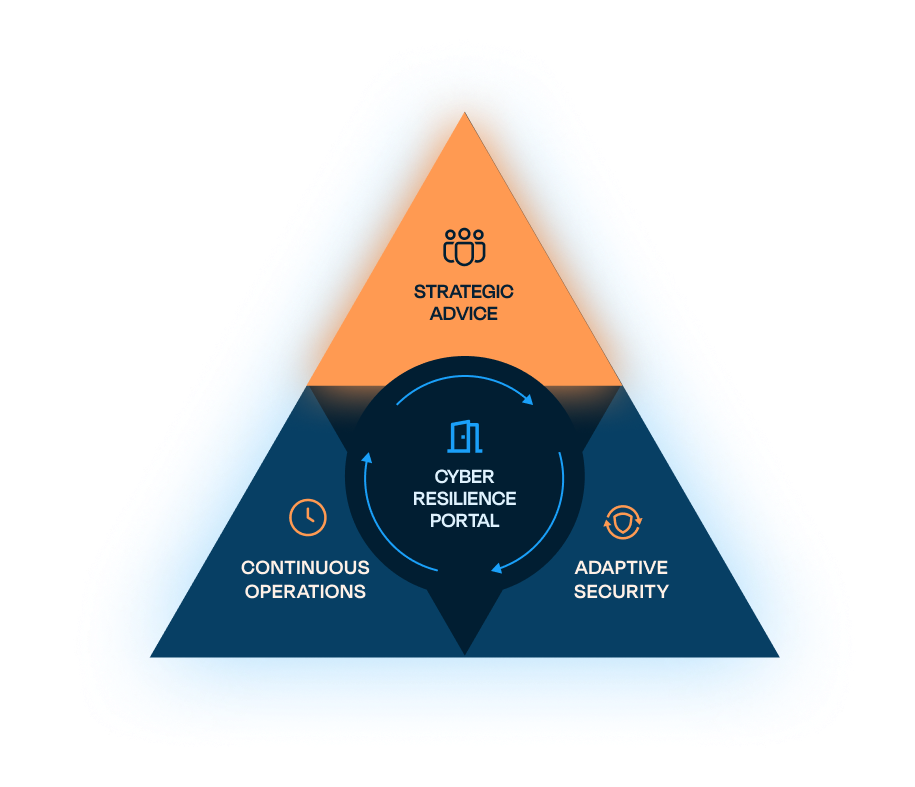
The Triangle of Cyber Resilience
Security Architecture is part of Strategic Advice, Approach Cyber’s pillar for strategy and people first, alongside Governance, Risk & Compliance (GRC). Where GRC tells you what to protect and which obligations apply, Security Architecture designs how your technical and operational layers hold together to meet them.