Your security tools generate more alerts than any internal team can realistically triage, and once an intrusion occurs, it can quickly evolve from initial access to full compromise in minutes. Building and staffing a 24/7 in-house Security Operations Center in-house is out of reach for most mid-sized organisations, yet NIS2, DORA and GDPR increasingly expect you to prove someone is watching. Without continuous monitoring, critical alerts will get lost in the noise.
Your concerns, our answers
Isn’t 24/7 monitoring only within reach of large enterprises?
Not any more. A Managed SOC gives mid-sized organizations 24/7 expert monitoring for a predictable, per-endpoint cost. No hiring required.
How do I know a real threat won’t get lost in all the noise?
Automated correlation filters the noise first; a human analyst validates every real alert before it reaches you, and recurring false positives can be suppressed entirely at your request.
Does outsourcing monitoring mean losing control of our NIS2 or DORA compliance?
No, you remain the accountable party. Our SOC operates under a documented governance framework, with regular reporting designed to support your NIS2, DORA and ISO 27001 evidence.
Running a SIEM no one has time to watch or drowning in alerts from disconnected tools?
Belgian-developed, EU-hosted SOC platform and SIEM, built with data sovereignty in mind.
Depending on your environment, we run your detection on our own in-house developed SIEM or on Microsoft Sentinel. In both cases, our SOC handles detection and response.
24/7 human-led threat hunting, supported by AI-based tooling, not replaced by it.
Trusted partner to the Centre for Cybersecurity Belgium (CCB), with active ties to KU Leuven, VUB and UCL.
Connect the dots across your entire attack surface. We provide continuous, correlated monitoring across endpoints, network, identity, cloud, and DNS to stop cross-system threats in their tracks.
Tier 1 to Tier 3 analysts and threat hunters validate every real alert and contain confirmed threats, pairing automated containment with human judgement rather than relying on either alone.
It continuously monitors your endpoints, network, identity, cloud and DNS traffic, correlates that telemetry into real alerts, and has an analyst investigate and contain anything confirmed as a genuine threat, around the clock.
Is a Managed SOC only worth it for large enterprises?
No, quite the opposite. Mid-sized organisations often get the most value: they are large enough to be a real target and to fall under NIS2, but rarely dispose of the budget or headcount to run a 24/7 in-house SOC.
Depending on severity, we act immediately through automated containment, such as isolating a compromised device, while analysts investigate in parallel. You are notified immediately and kept in the loop as threats are handled, ensuring complete visibility into your security posture.
Where is my data hosted, and what does that mean for GDPR?
With our Belgian-developed SIEM, your data stays in the EU. With Microsoft Sentinel, it stays in the region of your own Microsoft tenant.
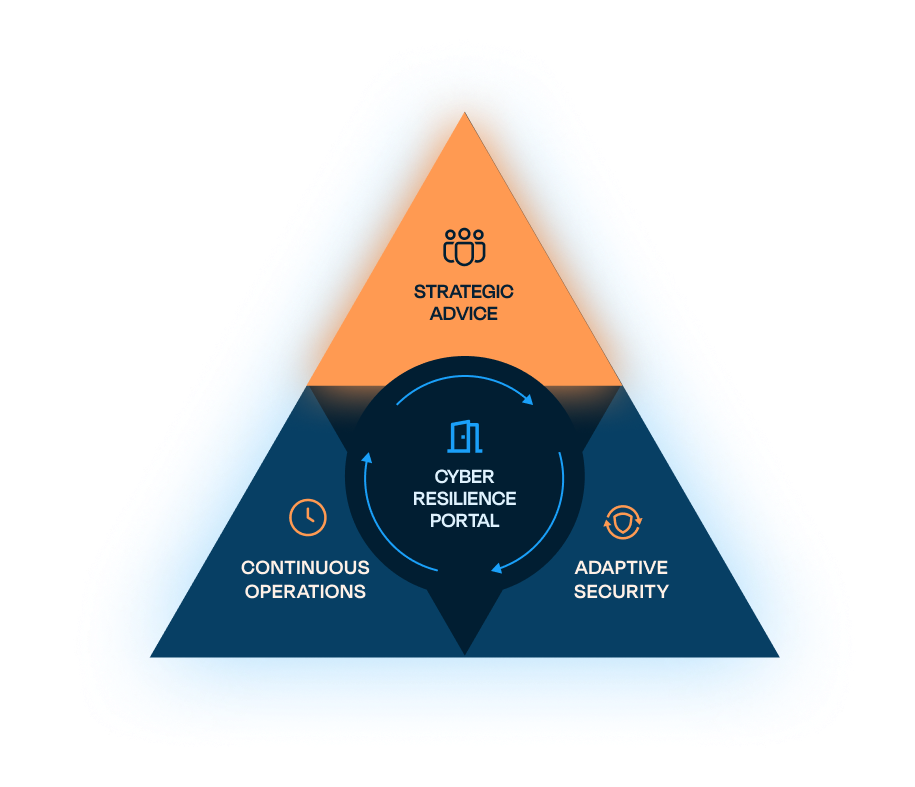
The Triangle of Cyber Resilience
Security Operations Center (SOC) is part of Continuous Operations, Approach Cyber’s pillar for ongoing vigilance and validation, alongside our Phishing & Awareness, Vulnerability & Exposure Management, Digital Forensics & Incident Response (DFIR), Managed Firewall Services and Offensive Security teams. Continuous Operations validates, in real time, what Strategic Advice designed and Adaptive Security enforced.